
Latest Tutorials
24 articles
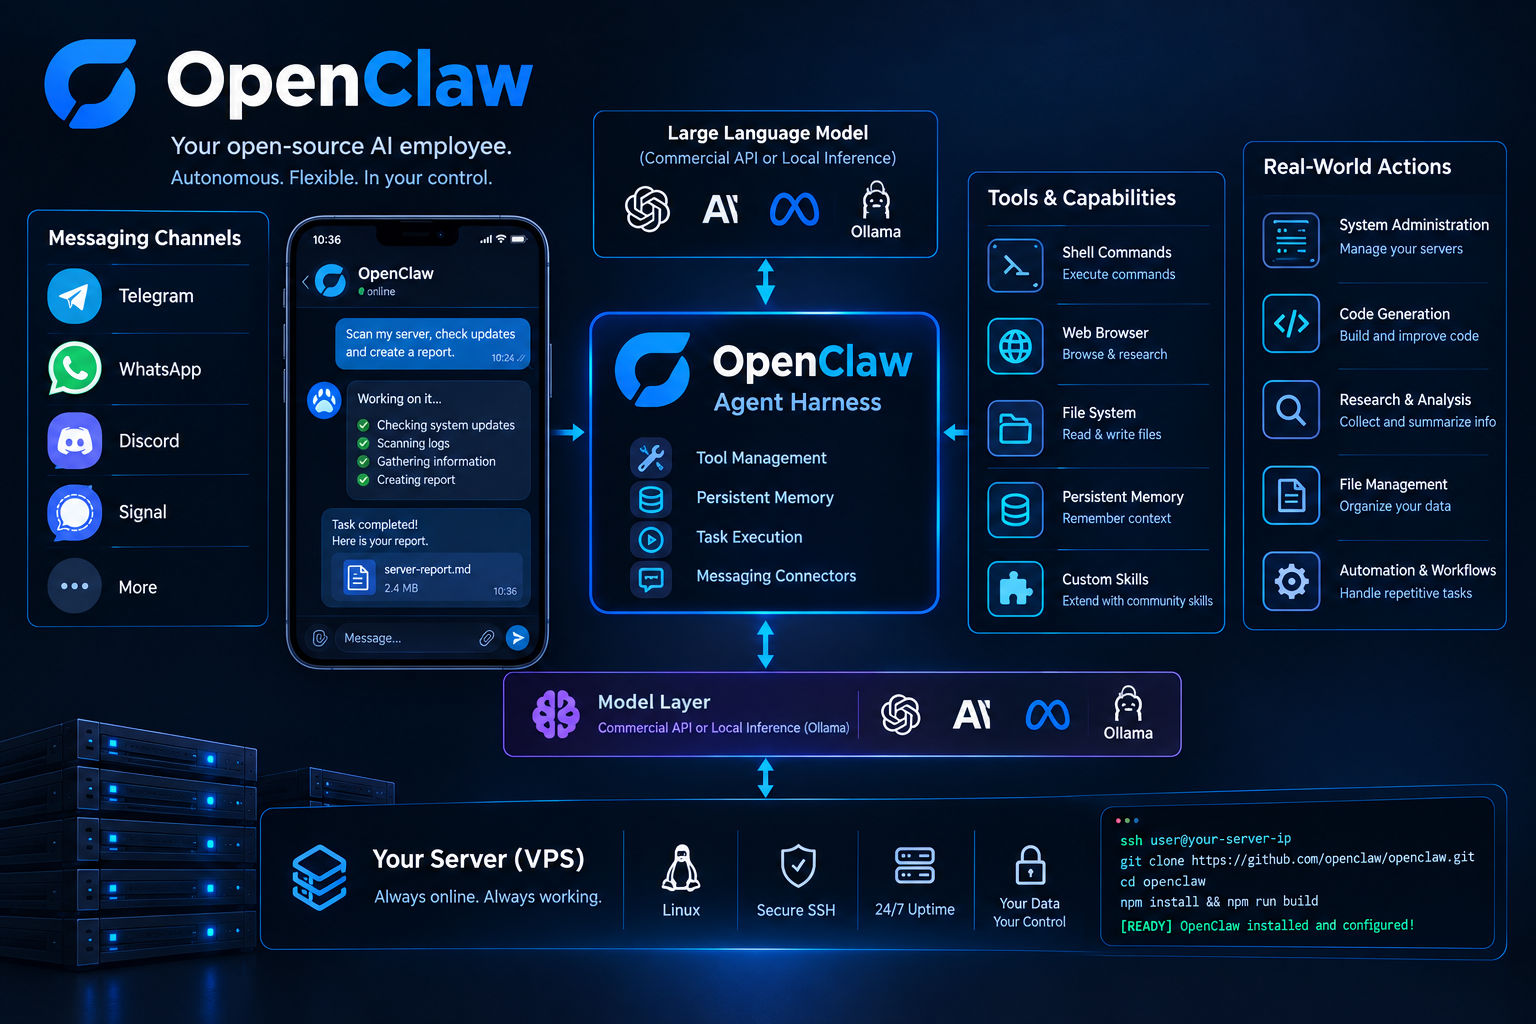
How to Build Your Own AI Employee Using OpenClaw
Build an open-source AI agent using OpenClaw on a VPS to automate tasks, connect messaging apps, execute shell commands, and manage daily workflows 24/7.
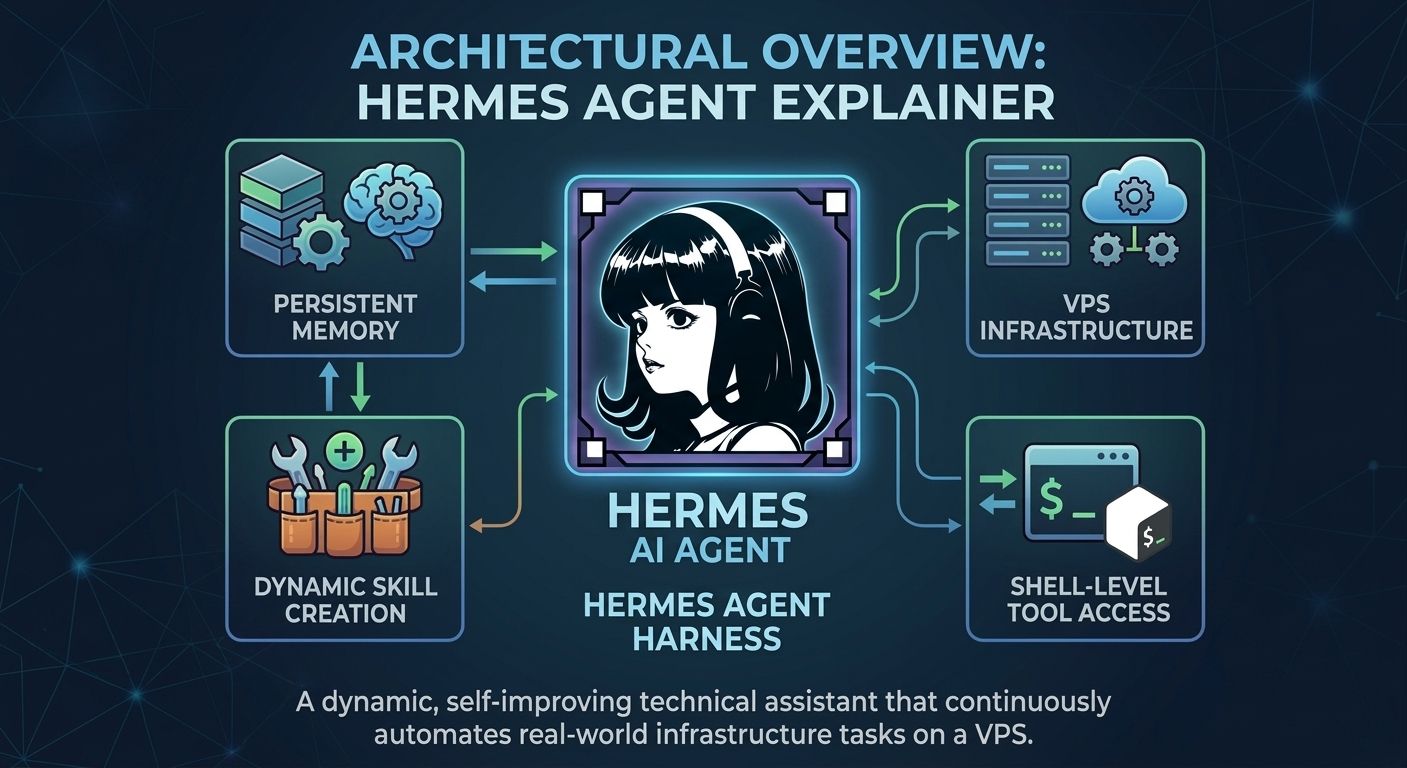
How to Build an Autonomous AI Assistant
Hermes is an open-source agent harness transforming static language models into self-improving technical assistants that automate infrastructure tasks.
Why Use Kubernetes? A Quick 5-Minute Guide
Kubernetes automates the deployment, scaling, and management of containerized applications, ensuring they run efficiently across server clusters.
What is Docker and how does it work ?
Docker solves deployment issues by packaging applications and dependencies into lightweight, isolated environments. This eliminates inconsistencies and speeds up modern software development.
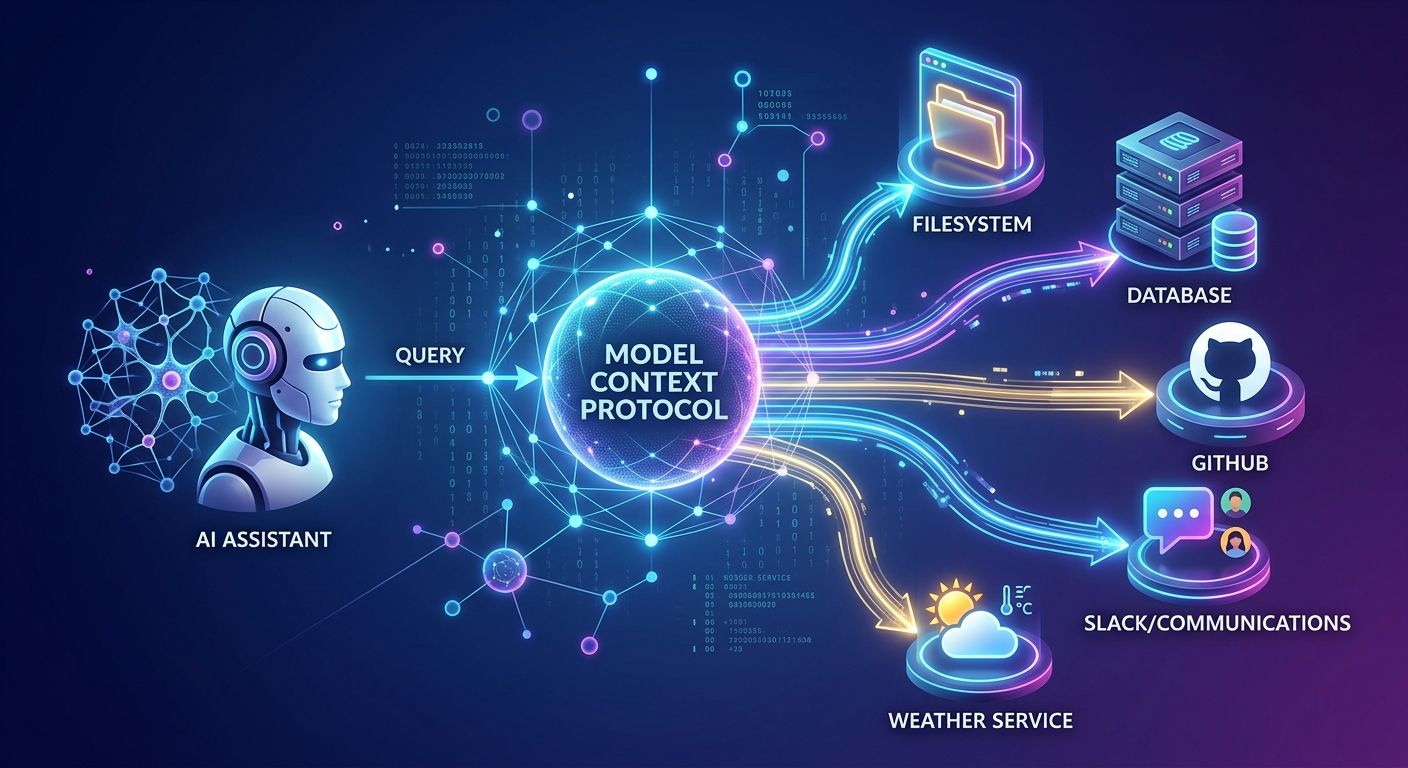
How MCP Connects AI Agents to External Tools
Context Protocol (MCP) is a standardized layer connecting AI applications to external tools, databases, and resources without custom API coding.
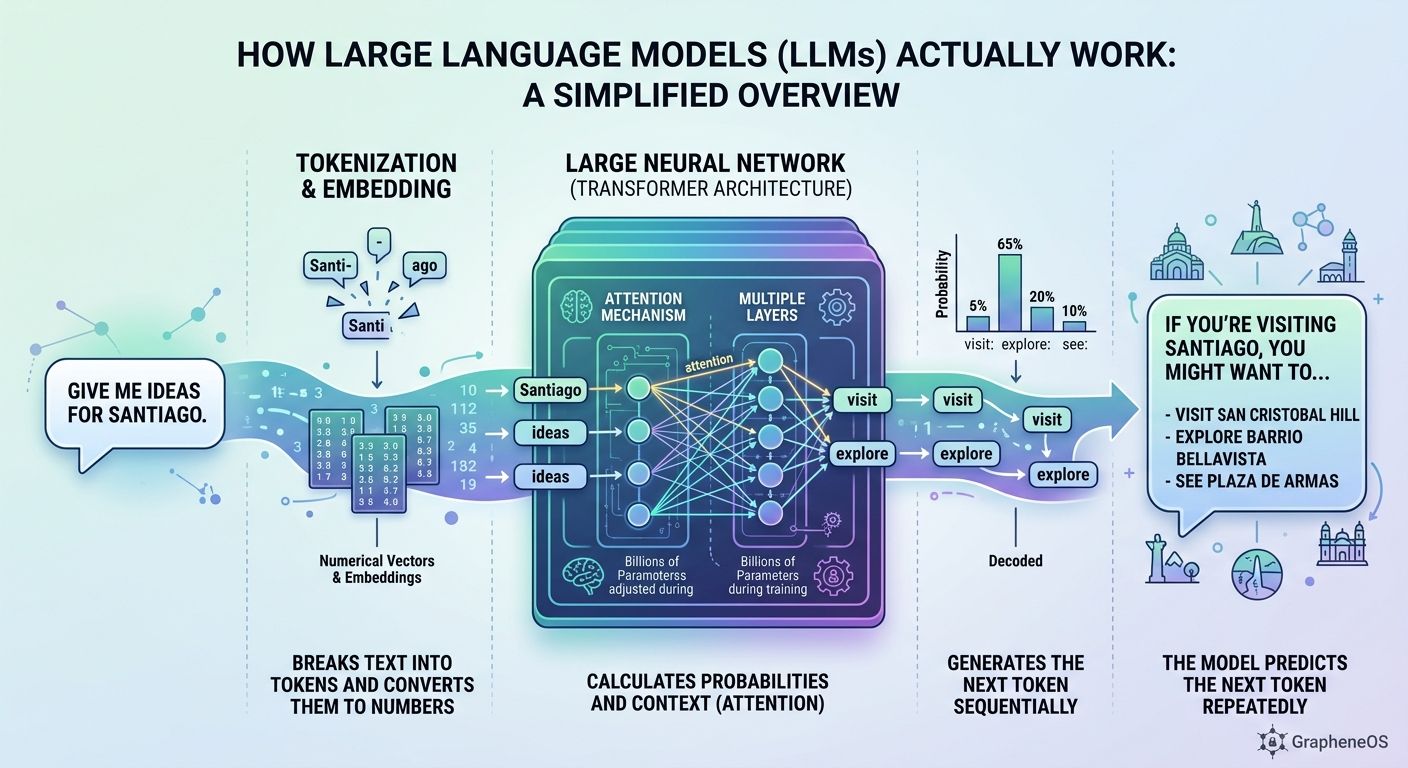
How Do Large Language Models Work? A Brief Look Inside AI
Large Language Models (LLMs) are massive neural networks trained to predict text one piece at a time. Rather than pulling pre-written answers from a database, they convert your prompts into mathematical representations and calculate the probability of the most likely next word, creating fluid and conversational responses.
How to Set Up Parental Controls on TikTok, Instagram, and YouTube
Protect your child online across major video and social platforms. Learn how to configure Family Pairing on TikTok, Supervision on Instagram, and Restricted Mode on YouTube with step-by-step instructions.
How to Install FSR 3.1 Frame Generation in Any Game: The 2026 Guide
Unlock massive FPS gains on NVIDIA, AMD, and Intel GPUs. Learn how to inject AMD's FSR 3.1 Frame Generation into your favorite titles using community translation layers, complete with command-line deployment instructions.
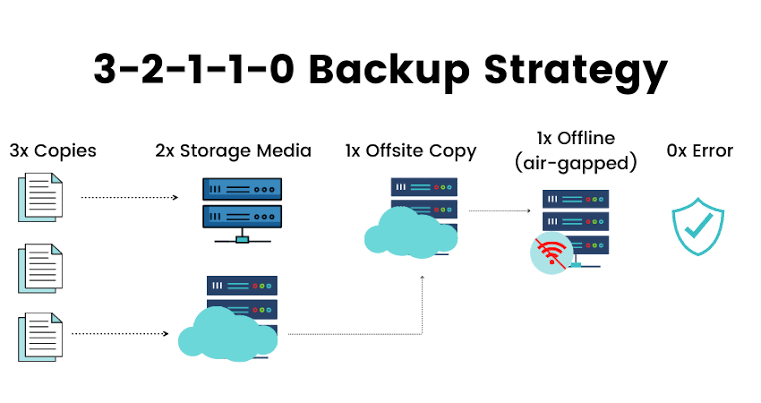
How to Stop Ransomware with 3-2-1 Backups
Master the 3-2-1-1-0 backup rule to stop ransomware. Learn how to mix local imaging, offsite storage, and immutable cloud copies, then test your restores.
How to Install DLSS 5 in Any Game: The One-Click Guide for RTX GPUs
Installing a cutting-edge performance mod across your entire PC gaming library no longer requires manual file swapping or editing config files.
How to Install Omarchy: AI Linux Desktop Guide
Omarchy is Arch Linux with Hyprland, Quickshell, and AI agents. Learn installation, theme customization, plugins, gaming, and AI troubleshooting .
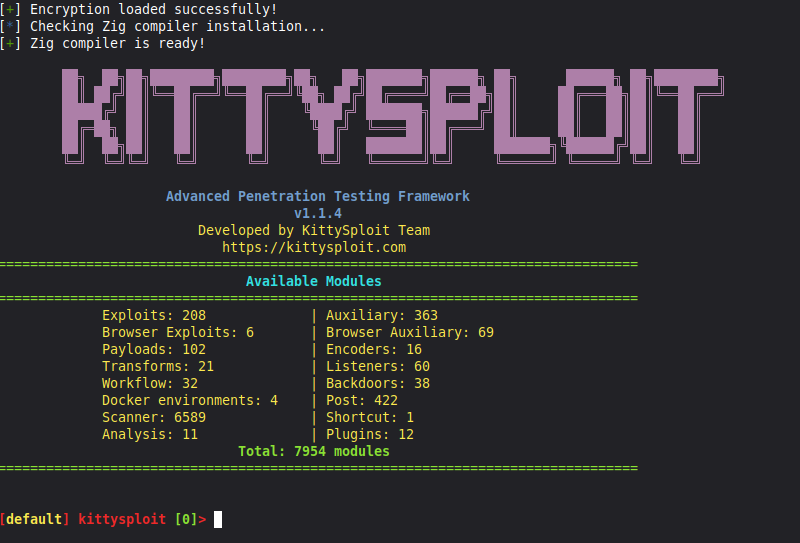
KittySploit
Modular console : search, configure and execute security modules.
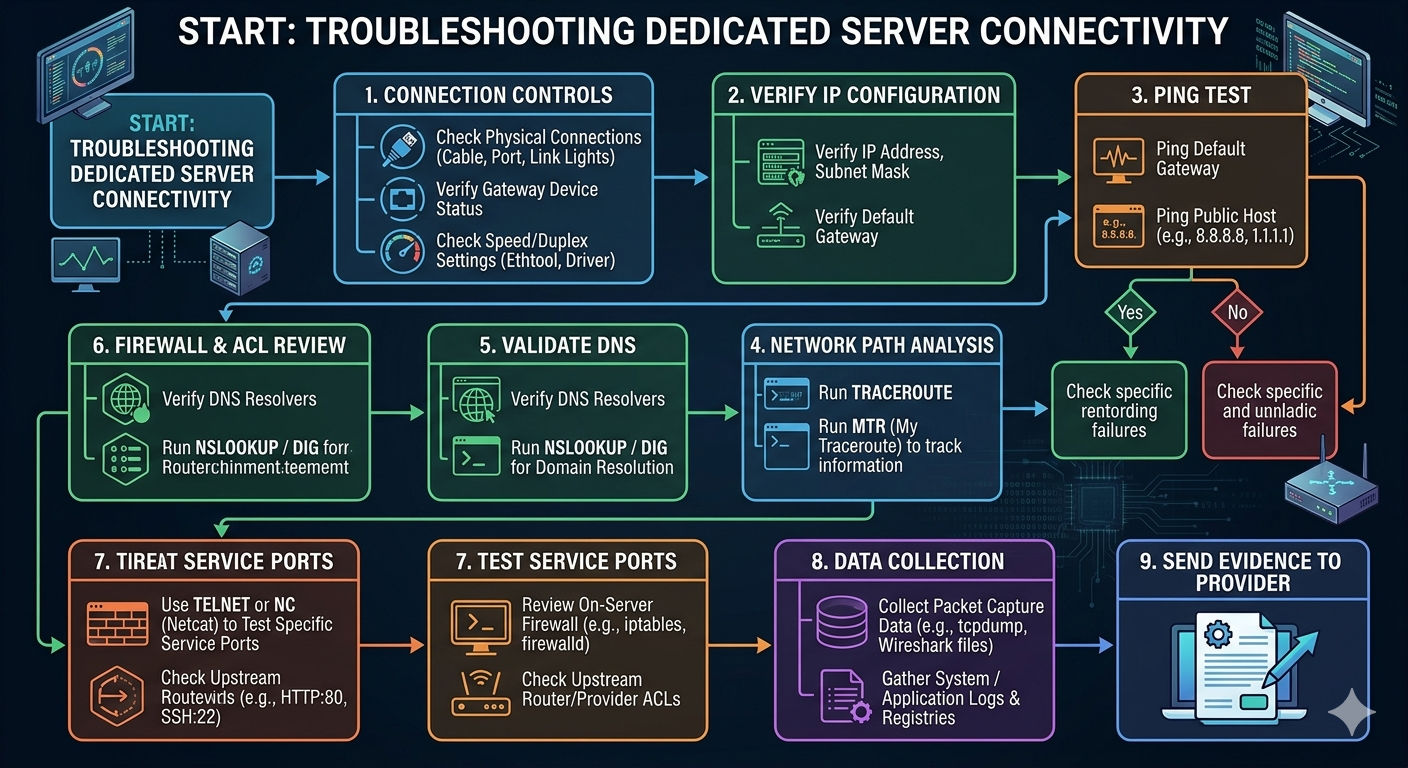
How to solve network connectivity problems on dedicated servers
To solve network connectivity problems on dedicated servers, start with connection controls (cable, gateway, speed/dupleks), verify IP/snut/gateway, make gateway ping and public hosts, run traceroute/MTR for tracking information, validate. DNS, review firewall/ACL rules, test specific service ports, and collect package capture data/registrees before sending the evidence to your provider.
What Is Penetration Testing
Penetration testing (pen testing) is a legal and authorized simulated cyber-attack on a computer system to evaluate its security. Pen testers act like real hackers: they use the same tools, techniques, and thinking to find and show weaknesses that could hurt the business.
What is Vulnerability Assessment
A vulnerability assessment is the process of checking a system to find security weaknesses. The goal is to know whether a system can be attacked, how dangerous the weakness is, and how to fix it.
Understanding Android Mobile Architecture and Its Security Vulnerabilities
Android is one of the most widely–used mobile operating systems in the world. To run smoothly on millions of devices, Android is built using a layered architecture. Each layer has a specific function that allows applications, system services, and hardware to work together.
Understanding what Threat, Vulnerability, Risk, Impact, Severity, and assesing Severity based on CVSS
A threat is anything that has the potential to do damage, even if the damage has not happened yet. In this case, a thief who walks around looking for houses to break into is the threat. The thief might or might not attack, but the possibility exists, and that possibility itself is the threat.
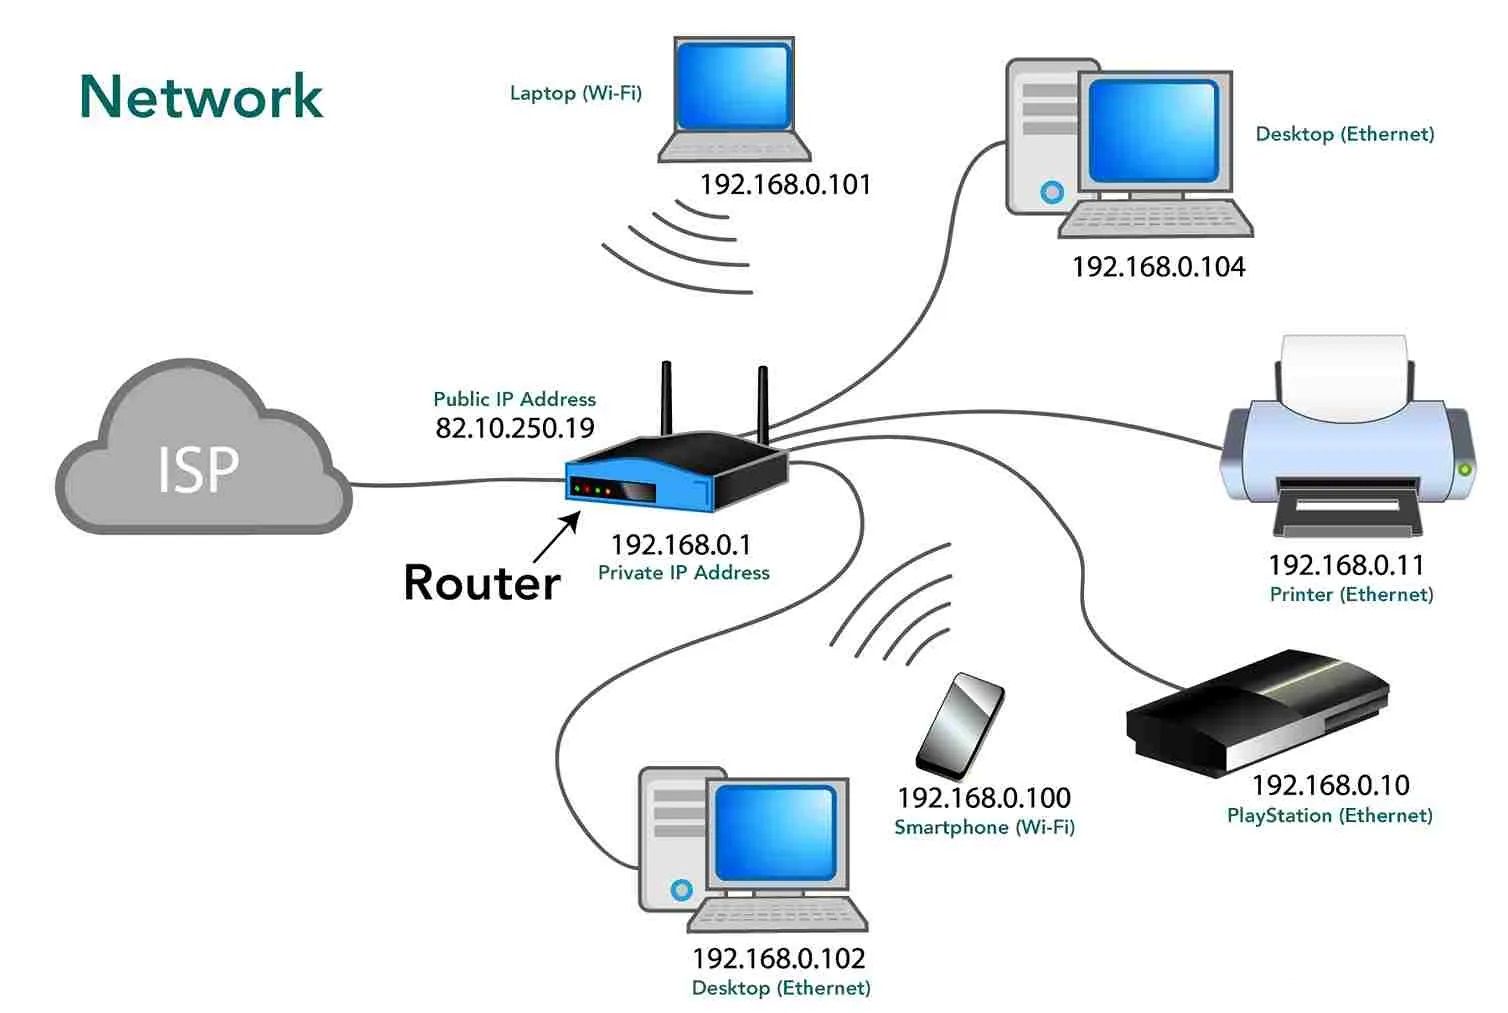
Understanding What IP, Port, and Protocol Is
This topic focuses on understanding the definitions of IP addresses, ports, and protocols, the differences between each of them, as well as commonly used standard ports and the network services that operate on those ports.
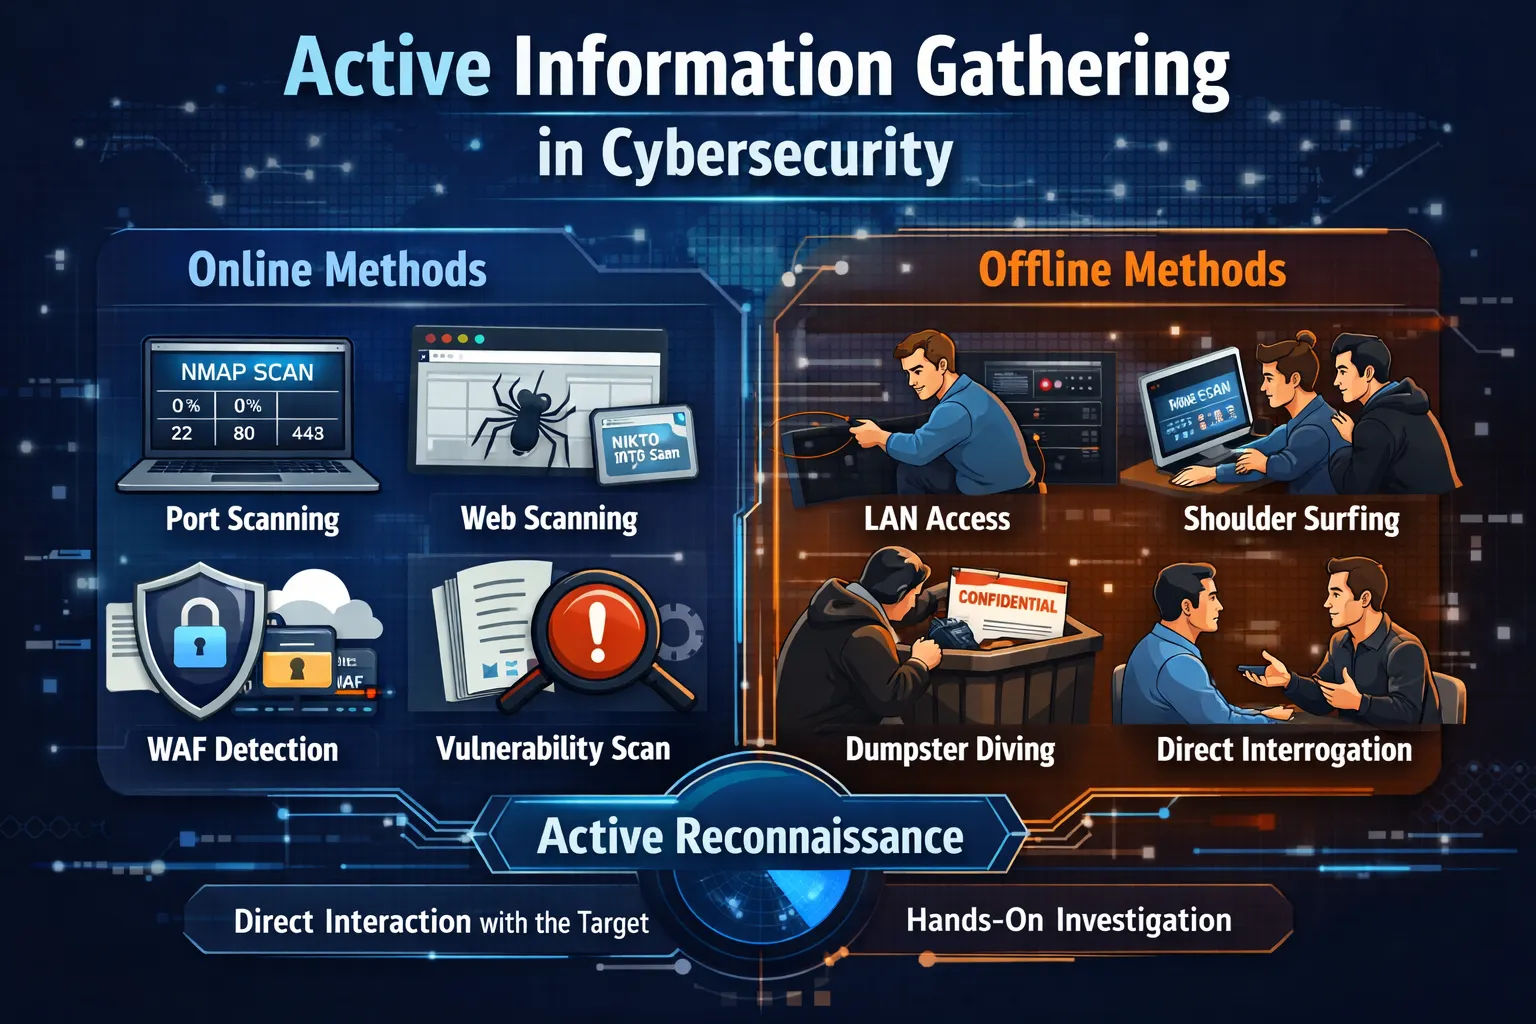
Active Information Gathering in Cybersecurity
In cybersecurity, the first phase of ethical hacking is called Reconnaissance or Information Gathering. This phase focuses on collecting information about a target before attempting any attack or security testing. Information gathering is divided into two main types: Passive Information Gathering Active Information Gathering
Captcha Bypass
Do not send the parameter related to the captcha. Check if the value of the captcha is in the source code of the page. Change some specific characters of the captcha parameter and see if it is possible to. When a new Captcha code is created, the previous code will expire.
Network Mapping for Beginners: Exploring Networks with Nmap
Network mapping is an early stage in network analysis, cybersecurity, and penetration testing activities. At this stage, the main objective is not to exploit vulnerabilities, but to understand the structure of the network. We want to know what devices exist, which hosts are active, and how the network is organized.
A Beginner’s Guide to Port Scanning Using Nmap
After identifying active hosts through network mapping, the next step is port scanning. Port scanning aims to determine which network services are running on each host.
Information Gathering in Cybersecurity
What is Information Gathering Information gathering is an important early step in cybersecurity and ethical hacking. It is the process of collecting and organizing information about a target system before performing deeper security testing.
Using Wordlists for Brute Force Attack in Kali Linux
A wordlist attack succeeds exactly when a password was predictable. Here is how they are chosen, built with crunch, and run through John and hashcat in a lab you own — and what each result tells you about defending against them.