
Everything we cover, in one place.
Browse categories, the newest articles, tutorials and quizzes. Built for professionals, businesses and curious learners.
Browse by category
8 topicsLatest articles
View all →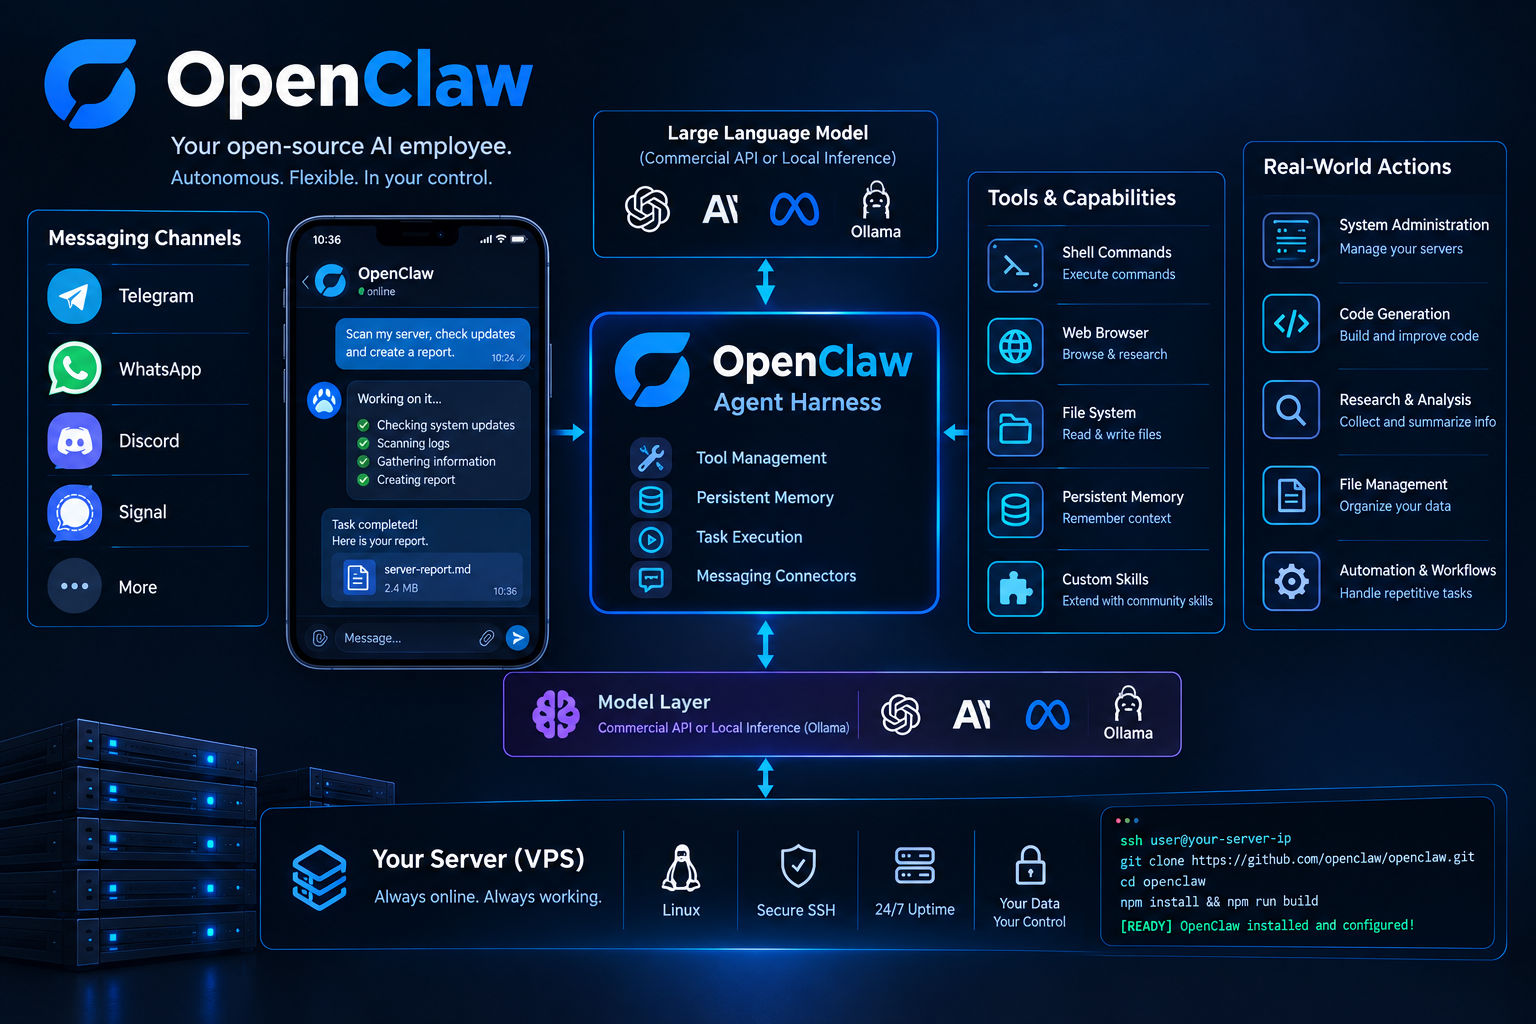 Latest Tutorials
How to Build Your Own AI Employee Using OpenClaw
Build an open-source AI agent using OpenClaw on a VPS to automate tasks, connect messaging apps, execute shell commands, and manage daily workflows 24/7.
 Latest Tutorials
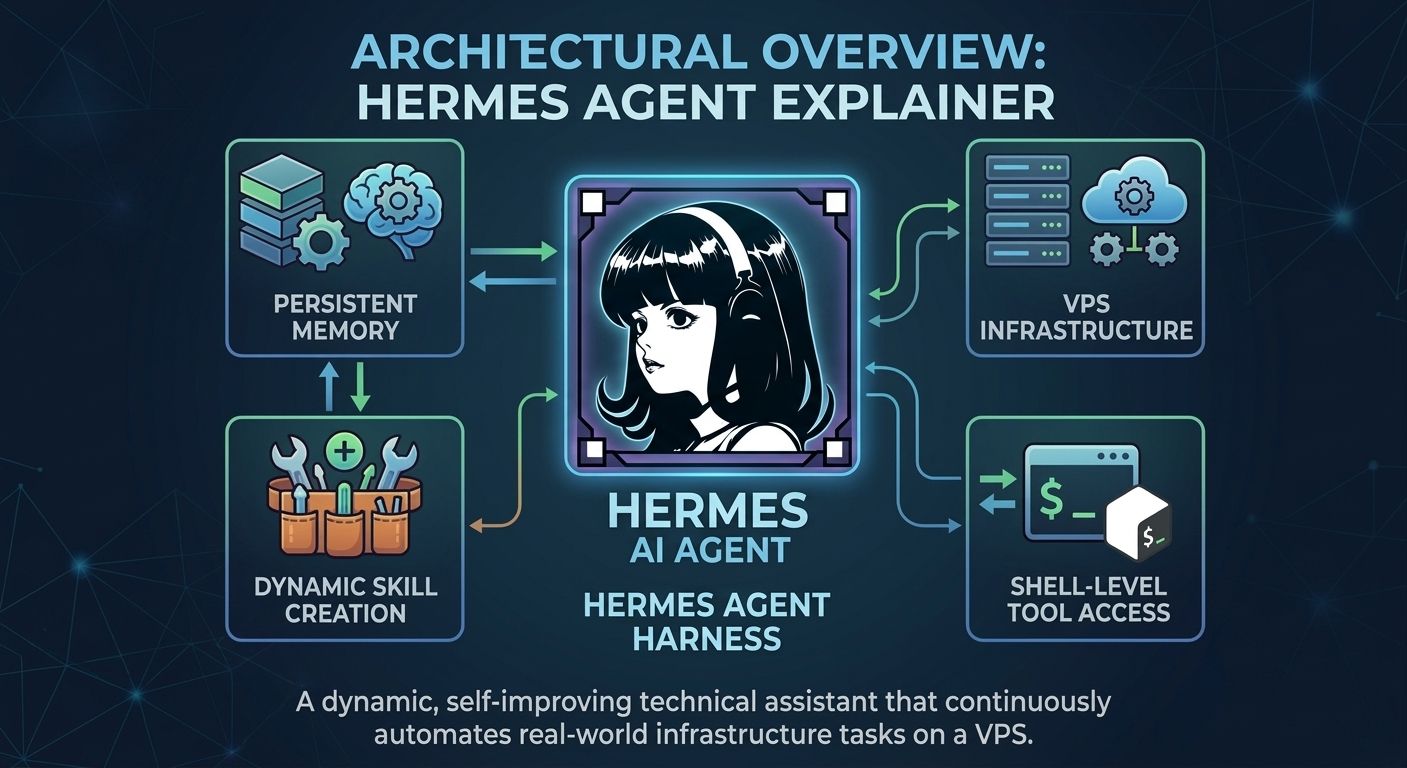
How to Build an Autonomous AI Assistant
Hermes is an open-source agent harness transforming static language models into self-improving technical assistants that automate infrastructure tasks.
 Latest Tutorials
Why Use Kubernetes? A Quick 5-Minute Guide
Kubernetes automates the deployment, scaling, and management of containerized applications, ensuring they run efficiently across server clusters.
 Latest Tutorials
What is Docker and how does it work ?
Docker solves deployment issues by packaging applications and dependencies into lightweight, isolated environments. This eliminates inconsistencies and speeds up modern software development.
 Latest Tutorials
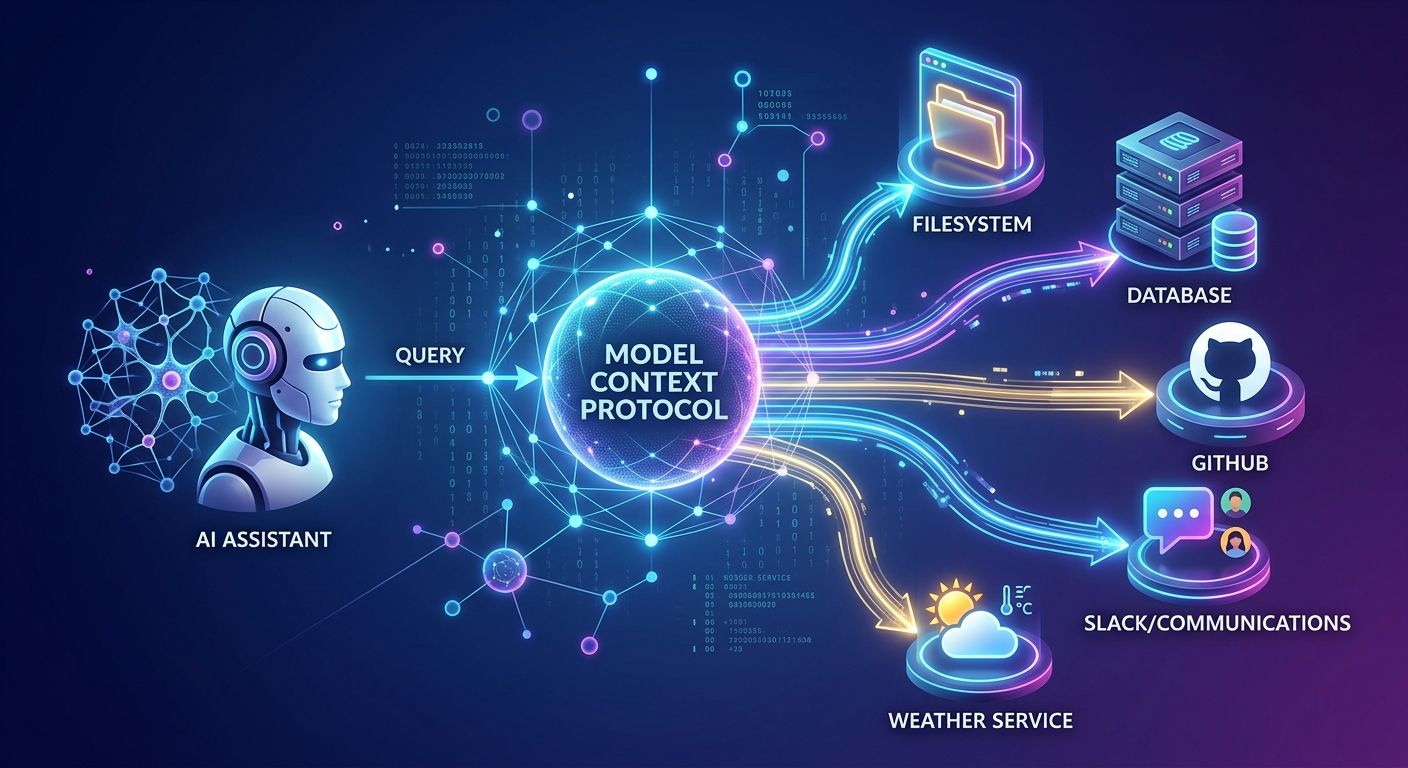
How MCP Connects AI Agents to External Tools
Context Protocol (MCP) is a standardized layer connecting AI applications to external tools, databases, and resources without custom API coding.
 Latest Tutorials
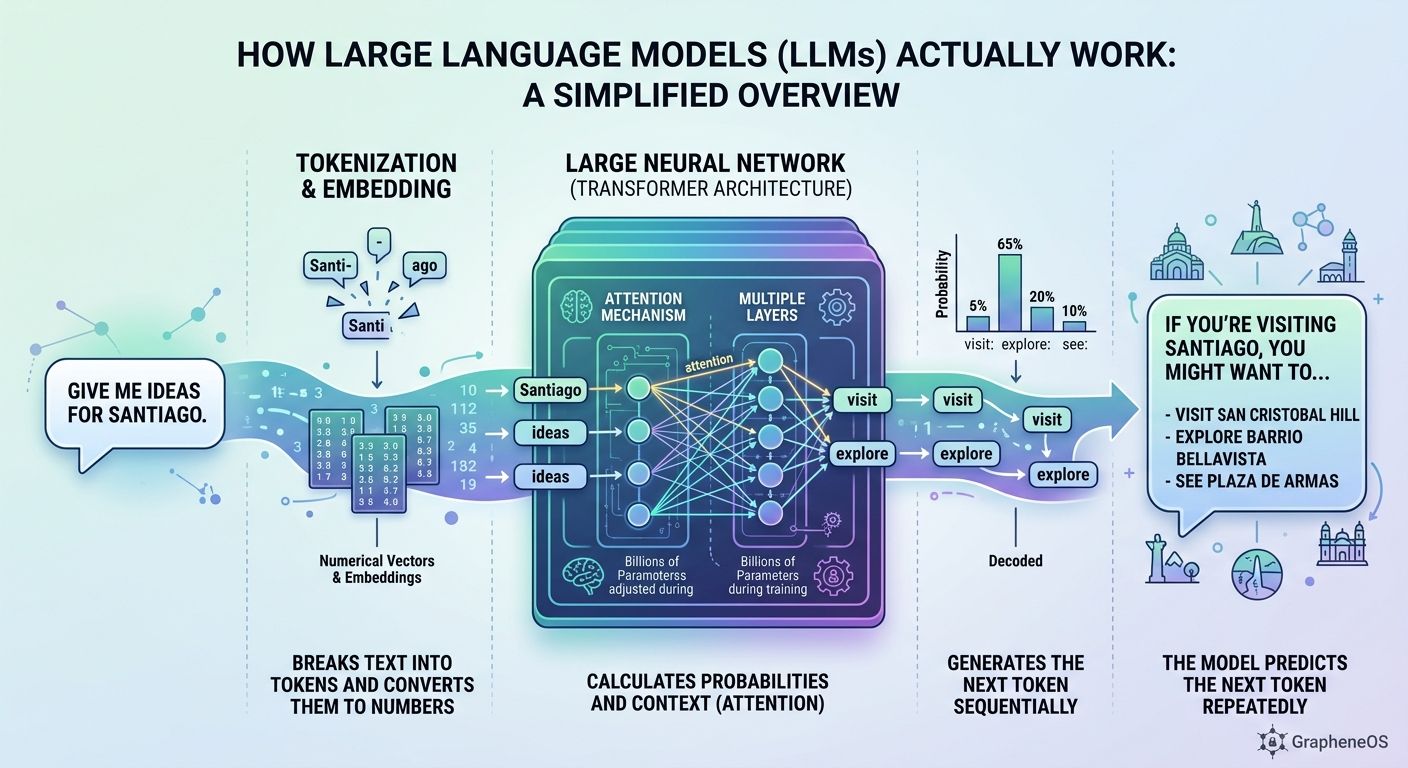
How Do Large Language Models Work? A Brief Look Inside AI
Large Language Models (LLMs) are massive neural networks trained to predict text one piece at a time. Rather than pulling pre-written answers from a database, they convert your prompts into mathematical representations and calculate the probability of the most likely next word, creating fluid and conversational responses.
 Android
How to Install GrapheneOS on a Google Pixel in 7 Steps
Installing GrapheneOS on a Google Pixel requires enabling OEM unlocking, entering Fastboot mode, and using the official Web Installer to flash the operating system. This straightforward process completely replaces your stock Android with a hardened, privacy-focused environment while maintaining physical security through Verified Boo
 Latest Tutorials
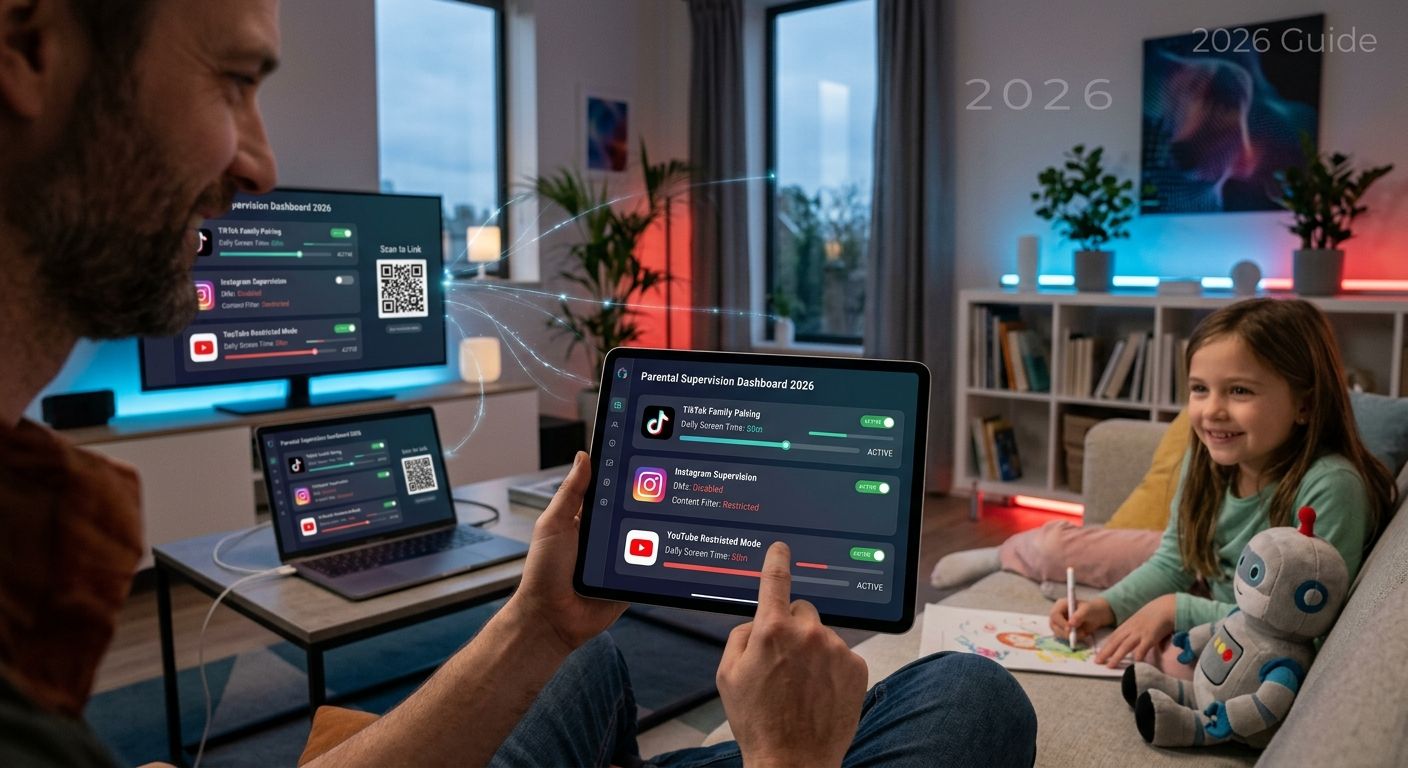
How to Set Up Parental Controls on TikTok, Instagram, and YouTube
Protect your child online across major video and social platforms. Learn how to configure Family Pairing on TikTok, Supervision on Instagram, and Restricted Mode on YouTube with step-by-step instructions.
 Windows
How to Install FSR 3.1 Frame Generation in Any Game: The 2026 Guide
Unlock massive FPS gains on NVIDIA, AMD, and Intel GPUs. Learn how to inject AMD's FSR 3.1 Frame Generation into your favorite titles using community translation layers, complete with command-line deployment instructions.
 Windows
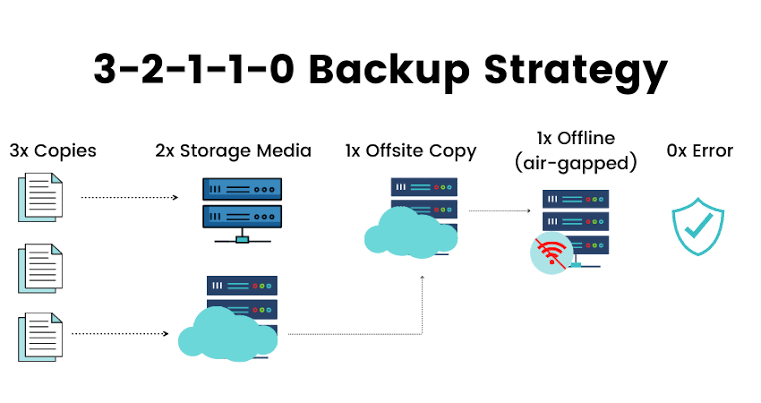
How to Stop Ransomware with 3-2-1 Backups
Master the 3-2-1-1-0 backup rule to stop ransomware. Learn how to mix local imaging, offsite storage, and immutable cloud copies, then test your restores.
 Windows
How to Install DLSS 5 in Any Game: The One-Click Guide for RTX GPUs
Installing a cutting-edge performance mod across your entire PC gaming library no longer requires manual file swapping or editing config files.
 Linux
How to Install Omarchy: AI Linux Desktop Guide
Omarchy is Arch Linux with Hyprland, Quickshell, and AI agents. Learn installation, theme customization, plugins, gaming, and AI troubleshooting .
 Windows
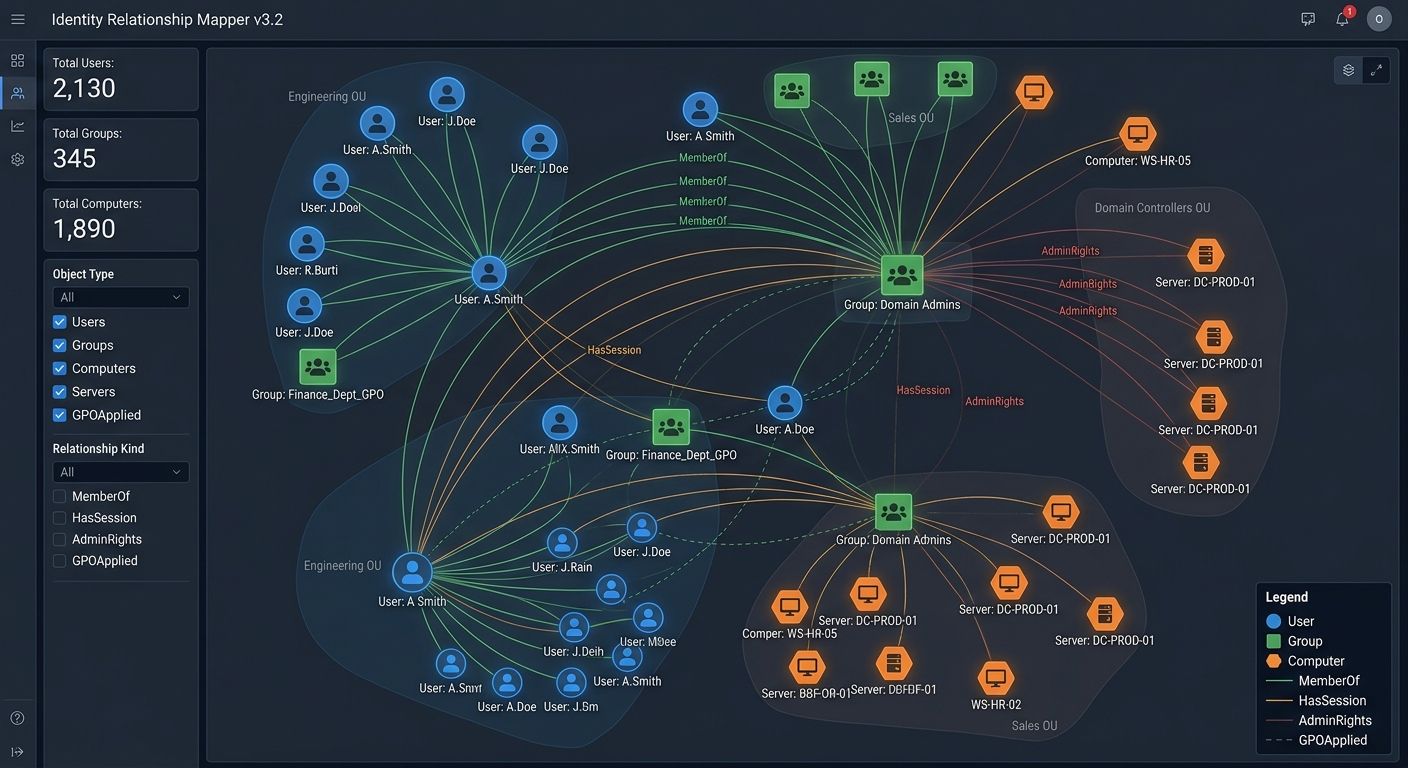
How BloodHound Helps Secure Active Directory
BloodHound maps Active Directory relationships to help defenders find excessive privileges, hidden access paths, and identity risks before they become problems.
 Linux
CVE-2026-19478: How to Detect and Mitigate GitLab's Critical 9.4 Code Injection Zero-Day
GitLab released an emergency out-of-band security patch to address CVE-2026-19478, a critical code injection vulnerability rating 9.4 on the CVSS scale. The flaw allows unauthenticated remote attackers to modify or delete public projects, rewrite repository state, and ban maintainers using a single crafted HTTP GraphQL request. Threat intelligence teams confirm that automated, AI-driven exploitation is actively reaching honeypots in the wild, making immediate patching or mitigation critical for
 Exploits
Active Zero-Day Alert: Microsoft Confirms Exploitation of CVSS 10.0 Entra ID Flaw Prior to Patch
On Thursday, Microsoft revealed that a critical remote code execution (RCE) vulnerability in Entra ID—the identity engine powering Microsoft 365, Azure, and Dynamics 365—was actively exploited in the wild prior to server-side mitigations. Tracked as CVE-2026-69836 and assigned a maximum CVSS score of 10.0, the flaw allows unauthenticated remote code execution. While Microsoft has patched the infrastructure, the lack of published indicators of compromise (IOCs) leaves enterprise defenders
 Latest Tutorials
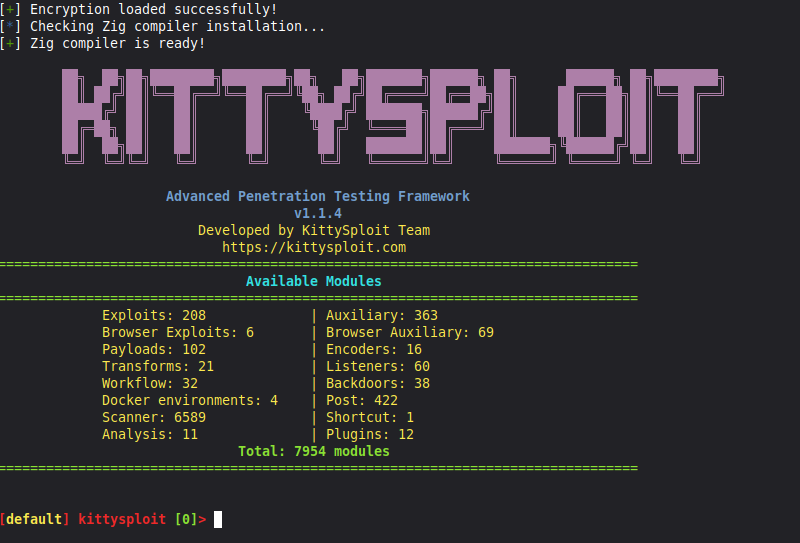
KittySploit
Modular console : search, configure and execute security modules.
 Linux
Linux Firewalls: What You Need to Know About iptables and firewalld
In the Linux ecosystem, packet filtering and network address translation (NAT) happen inside the kernel via frameworks like Netfilter and nftables .
 Linux
How to Install Nginx on Ubuntu: PPA/Official Repository, UFW Firewall, and Configuration Structure
An active Ubuntu server instance (Ubuntu 24.04 LTS / 26.04 LTS).