
SysAlbania
CyberSecurity
SysAlbania is a cyber security education platform and services team. We publish hands-on guides to penetration testing, bug bounty, red teaming and threat hunting, maintain a library of free open-source security tooling, and track newly disclosed vulnerabilities. Everything we publish is written from our own testing: our own screenshots, our own command output, our own lab work. Alongside the free content we carry out paid security assessments for clients, and what we learn doing that work is what ends up here. All content is published for education and for authorised testing only.
Articles by SysAlbania
32 articles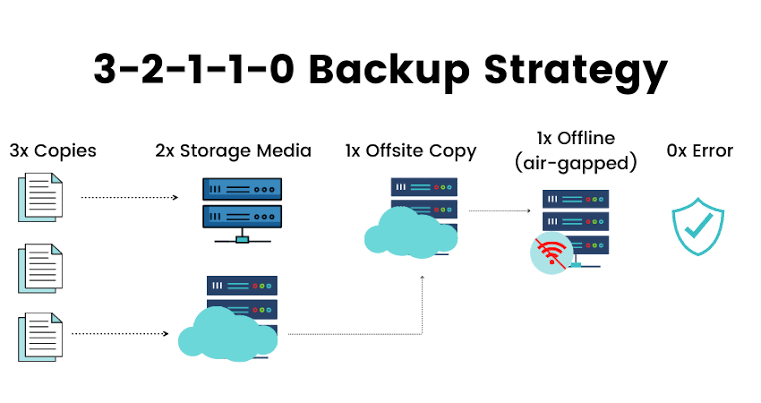 Windows
How to Stop Ransomware with 3-2-1 Backups
Master the 3-2-1-1-0 backup rule to stop ransomware. Learn how to mix local imaging, offsite storage, and immutable cloud copies, then test your restores.
 Windows
How to Install DLSS 5 in Any Game: The One-Click Guide for RTX GPUs
Installing a cutting-edge performance mod across your entire PC gaming library no longer requires manual file swapping or editing config files.
 Linux
How to Install Omarchy: AI Linux Desktop Guide
Omarchy is Arch Linux with Hyprland, Quickshell, and AI agents. Learn installation, theme customization, plugins, gaming, and AI troubleshooting .
 Windows
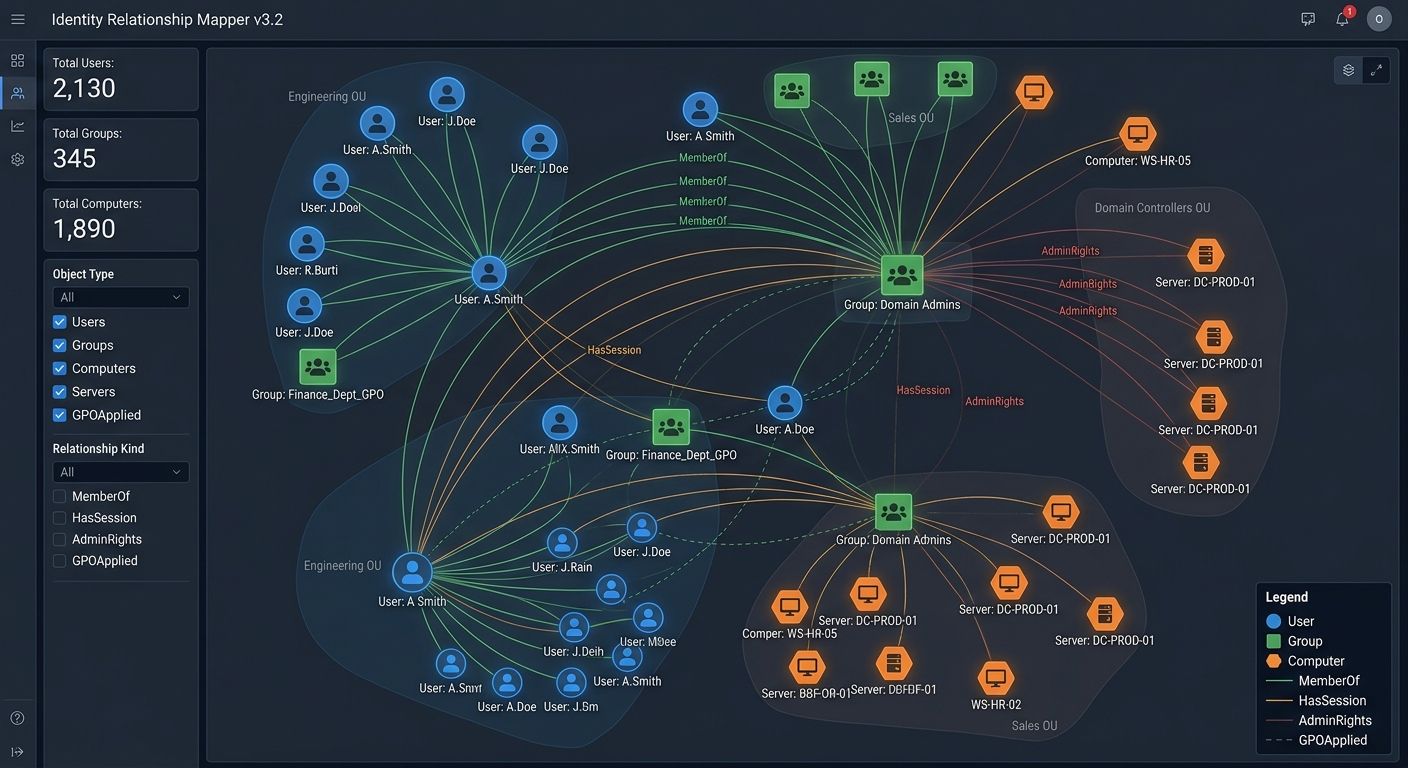
How BloodHound Helps Secure Active Directory
BloodHound maps Active Directory relationships to help defenders find excessive privileges, hidden access paths, and identity risks before they become problems.
 Linux
CVE-2026-19478: How to Detect and Mitigate GitLab's Critical 9.4 Code Injection Zero-Day
GitLab released an emergency out-of-band security patch to address CVE-2026-19478, a critical code injection vulnerability rating 9.4 on the CVSS scale. The flaw allows unauthenticated remote attackers to modify or delete public projects, rewrite repository state, and ban maintainers using a single crafted HTTP GraphQL request. Threat intelligence teams confirm that automated, AI-driven exploitation is actively reaching honeypots in the wild, making immediate patching or mitigation critical for
 Exploits
Active Zero-Day Alert: Microsoft Confirms Exploitation of CVSS 10.0 Entra ID Flaw Prior to Patch
On Thursday, Microsoft revealed that a critical remote code execution (RCE) vulnerability in Entra ID—the identity engine powering Microsoft 365, Azure, and Dynamics 365—was actively exploited in the wild prior to server-side mitigations. Tracked as CVE-2026-69836 and assigned a maximum CVSS score of 10.0, the flaw allows unauthenticated remote code execution. While Microsoft has patched the infrastructure, the lack of published indicators of compromise (IOCs) leaves enterprise defenders
 Latest Tutorials
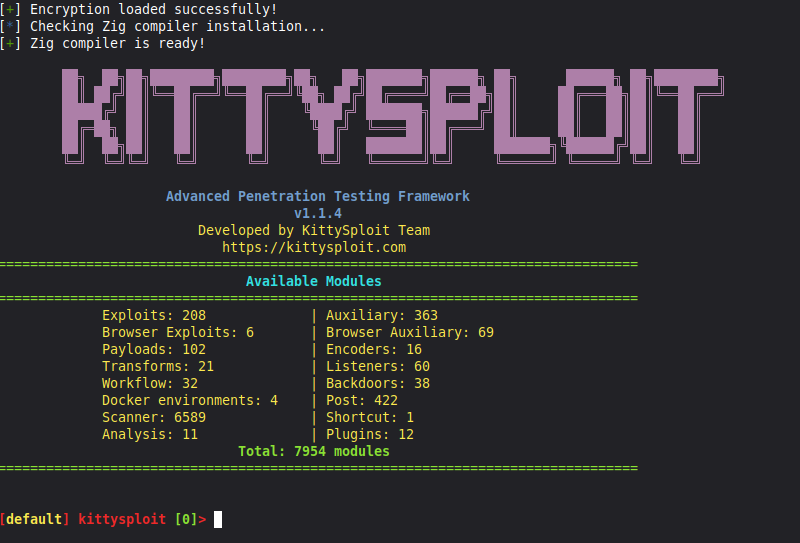
KittySploit
Modular console : search, configure and execute security modules.
 Network Security
AI-Generated Malware Campaign Scales Threats Through Vibe Coding Techniques
Normal 0 false false false false EN-US X-NONE X-NONE The campaign consists of more than 440 malicious ZIP archives distributed across…
 Network Security
How AI Puts Data Security at Risk
However, it also brings significant risks to data security.